IntroToBurp (Easy)
- Challenge Link: https://play.picoctf.org/practice/challenge/419?bookmarked=0&category=1&difficulty=1&page=1&solved=0
- Challenge Description: N/A
Solution
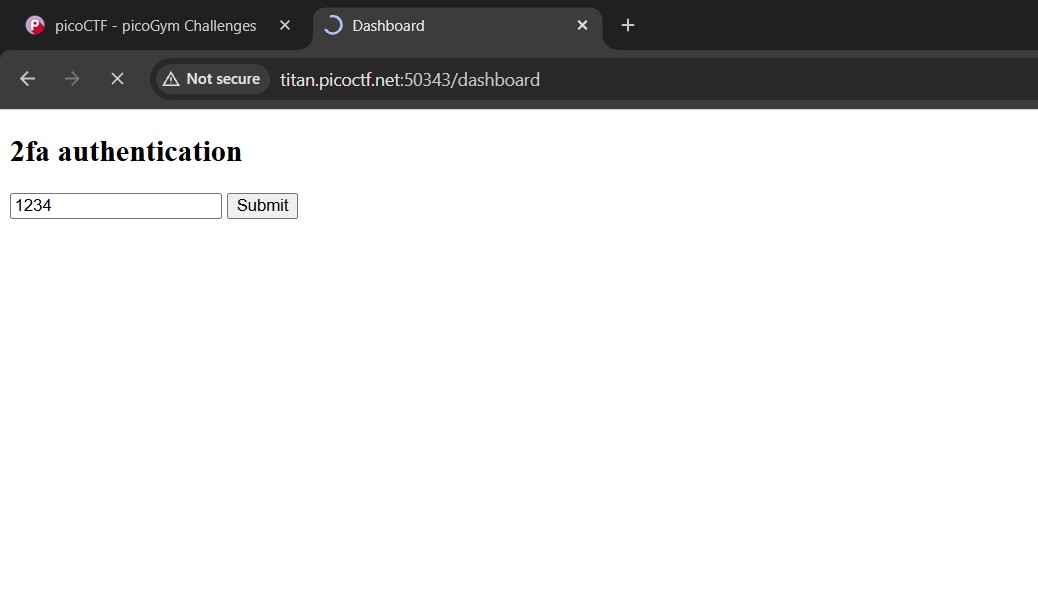
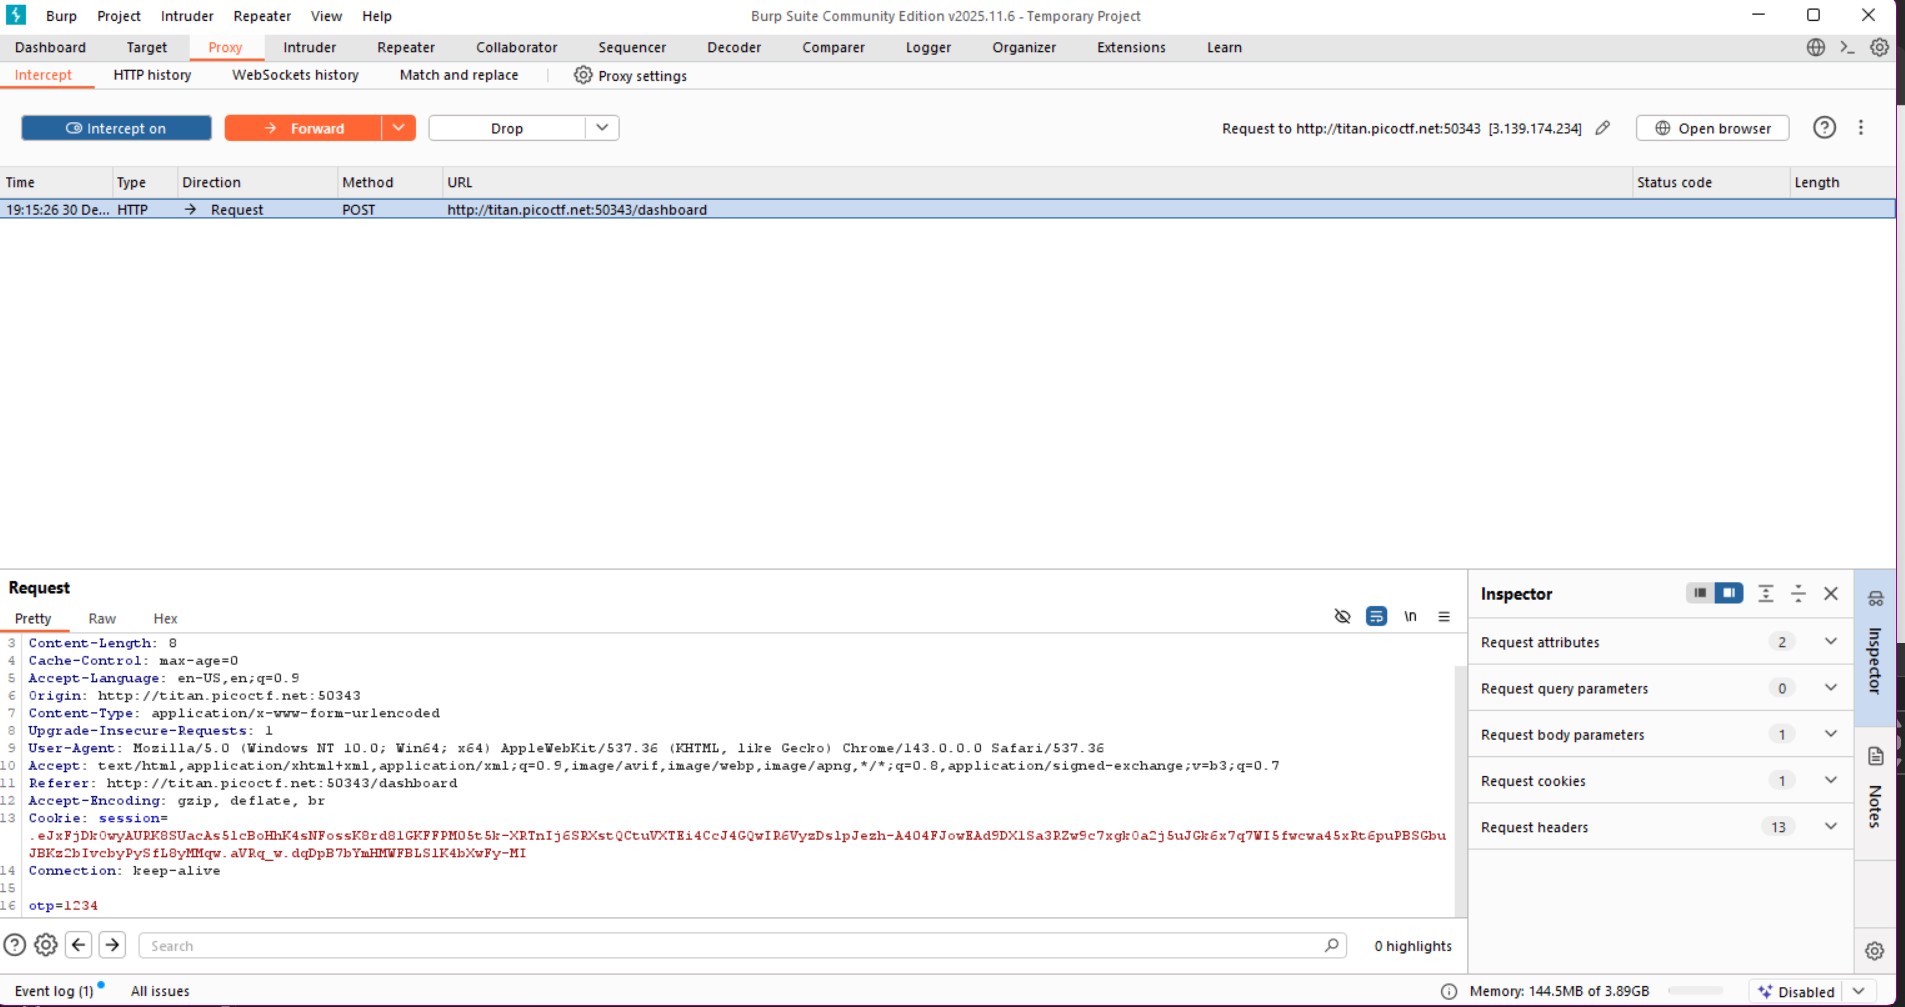
To find the flag, we need to use Burp Suite (refer to my GET aHEAD to know what Burp Suite is), basically, we need to modify our requests again. In this challenge, we try to login by using random credentials but after that we need our 2FA code, which we don't have. But, if we put a random 2FA code and using BurpSuite to intercept our request then delete our OTP, it's almost as if we put the correct code and we get access.