Old Sessions (Easy)
- Challenge Link: https://learn.cylabacademy.org/library/739?page=1&category=1&search=ol
- Challenge Description: Proper session timeout controls are critical for securing user accounts. If a user logs in on a public or shared computer but doesn’t explicitly log out (instead simply closing the browser tab), and session expiration dates are misconfigured, the session may remain active indefinitely. This then allows an attacker using the same browser later to access the user’s account without needing credentials, exploiting the fact that sessions never expire and remain authenticated.
- Hints:
- Do you know how to use the web inspector?
- Where are cookies stored?
Solution
It's been a while (a couple months since I did some CTFs), it would appear that PicoCTF is going through some renovations? Looks pretty sick.
This is the home page of the site.
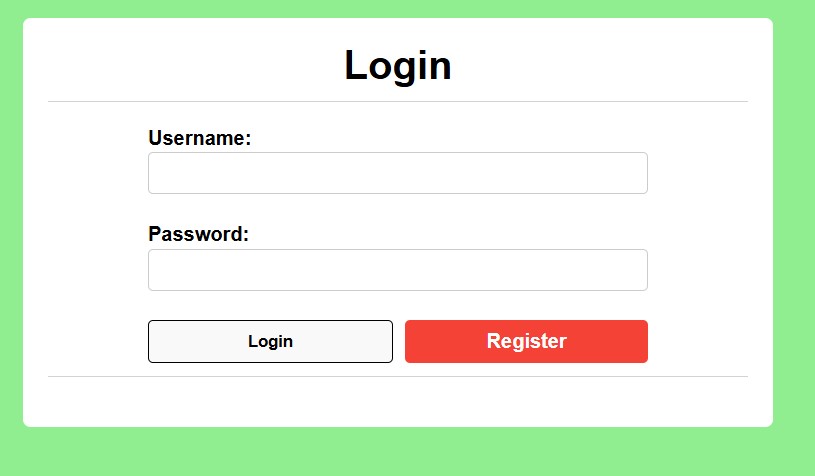
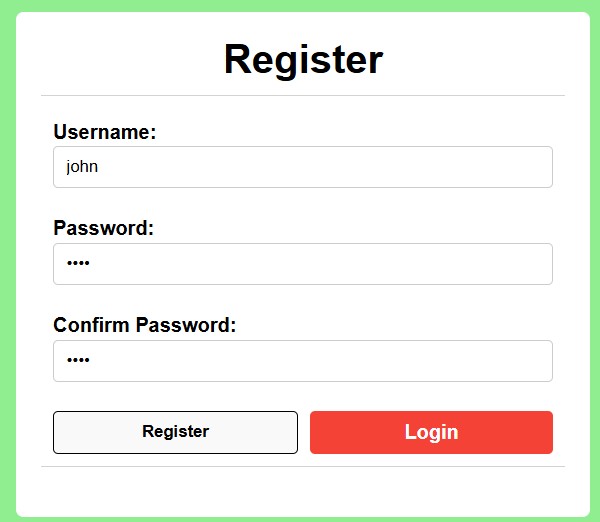
We could login but we do not have any accounts to work with, so let us register an account.
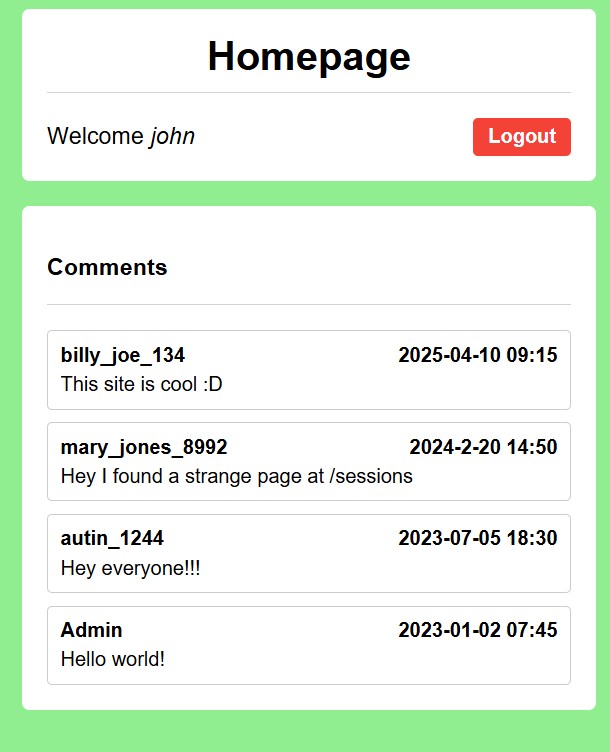
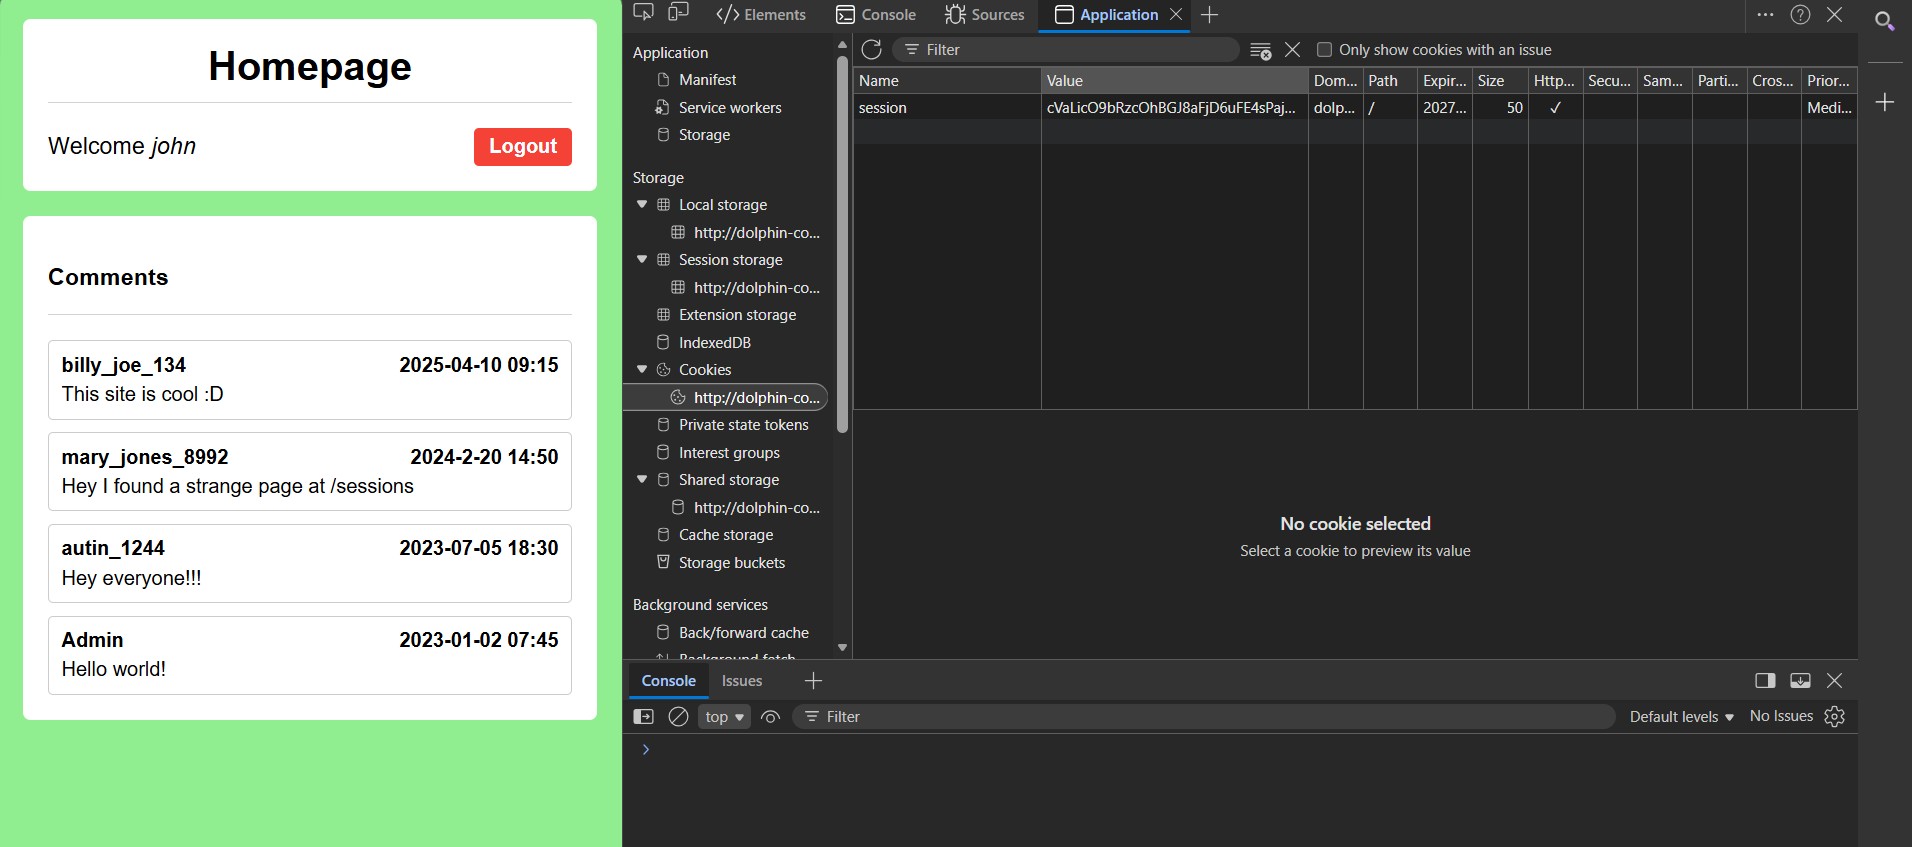
This is what we see after we register an account and log in. Someone in the forums mention that there is a weird page in /sessions.
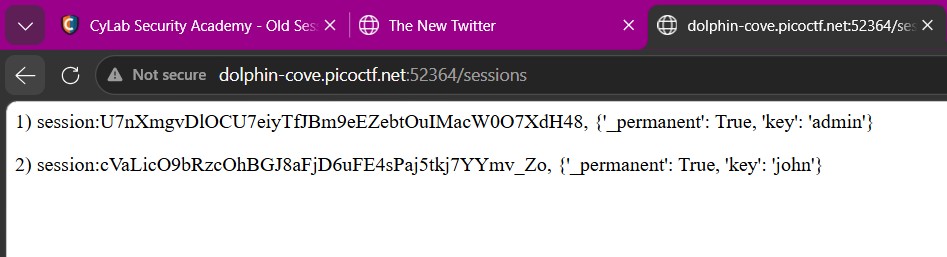
We can see the token associated with the admin, now all we need to do is to replace our token with the admins and we should have access.
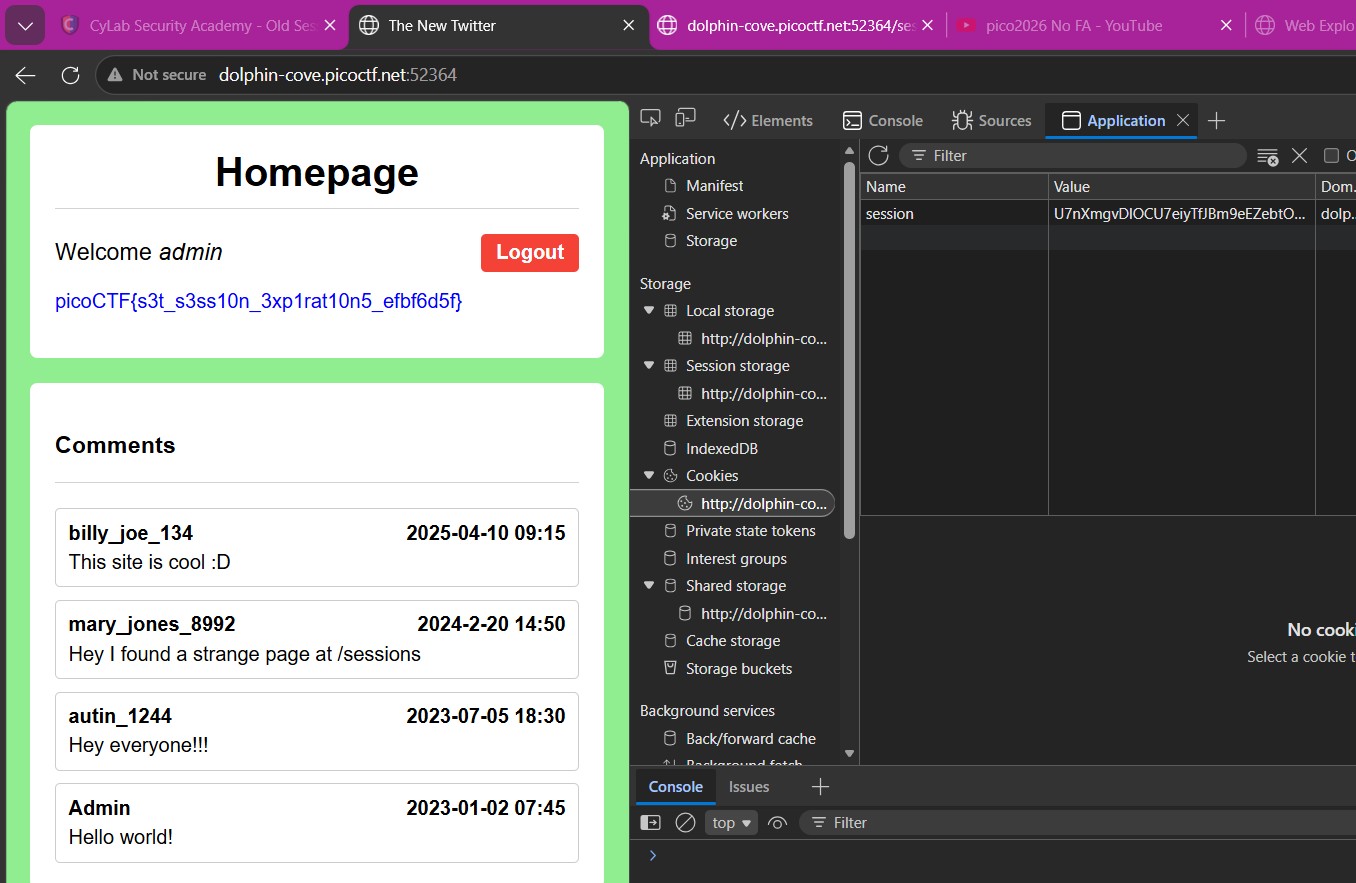
Flag: picoCTF{s3t_s3ss10n_3xp1rat10n5_efbf6d5f}
Sources
- N/A